Doocat

Open Banking API Provider Selection Guide for Banks and Fintechs

Content authorBy DoocatPublished onReading time14 min read
A business analyst in an executive suite discusses market data on a tablet with a colleague, surrounded by a modern office setting.

This article explains how to turn product and regulatory requirements into a selection process you can defend with evidence. It covers provider models and a weighted scorecard your teams can fill in together.

Why provider choice decides the rollout

Choosing an open banking API provider looks like a procurement exercise until the first production incident, when it becomes an architecture decision you can't unwind cheaply. The contract fixes your bank connectivity coverage and how much of the support burden lands on your own on-call rota.

Most comparisons never get past headline numbers. Plaid says it connects to more than 12,000 financial institutions across the US and Europe. That figure tells you nothing about whether the twenty banks your customers actually use will authenticate reliably at nine on a Monday morning.

So this guide works the other way round. Start with what you're launching and translate that into criteria you can test.

Define rollout requirements

Write down the markets first, because everything else narrows from there. A lender operating only in Ireland and Poland has a different shortlist from a payables product covering fifteen European countries, and the difference isn't a matter of degree.

Then pin down the journeys. Account data and payment initiation are separate regulatory permissions with separate failure modes, and an open banking API provider strong at one is not automatically strong at the other. Yapily's own comparison notes that TrueLayer requires using PIS to access its data features, which is exactly the kind of coupling that surfaces late if you don't ask early.

Your compliance position shapes the shortlist as much as your product does. If you don't hold your own permissions, you're either partnering or operating as an agent, and Yapily notes that agency applications are faster than full authorization and take weeks rather than months. That choice constrains which providers can serve you at all.

Now split the list in two:

  • Launch-critical: the markets and account types you cannot go live without.

  • Future preference: the extra countries and enrichment features you'd like within eighteen months.

Keep the second list visible but out of the scoring weights. Otherwise an open banking API provider wins on capabilities you won't use for two years.

Open banking API provider models

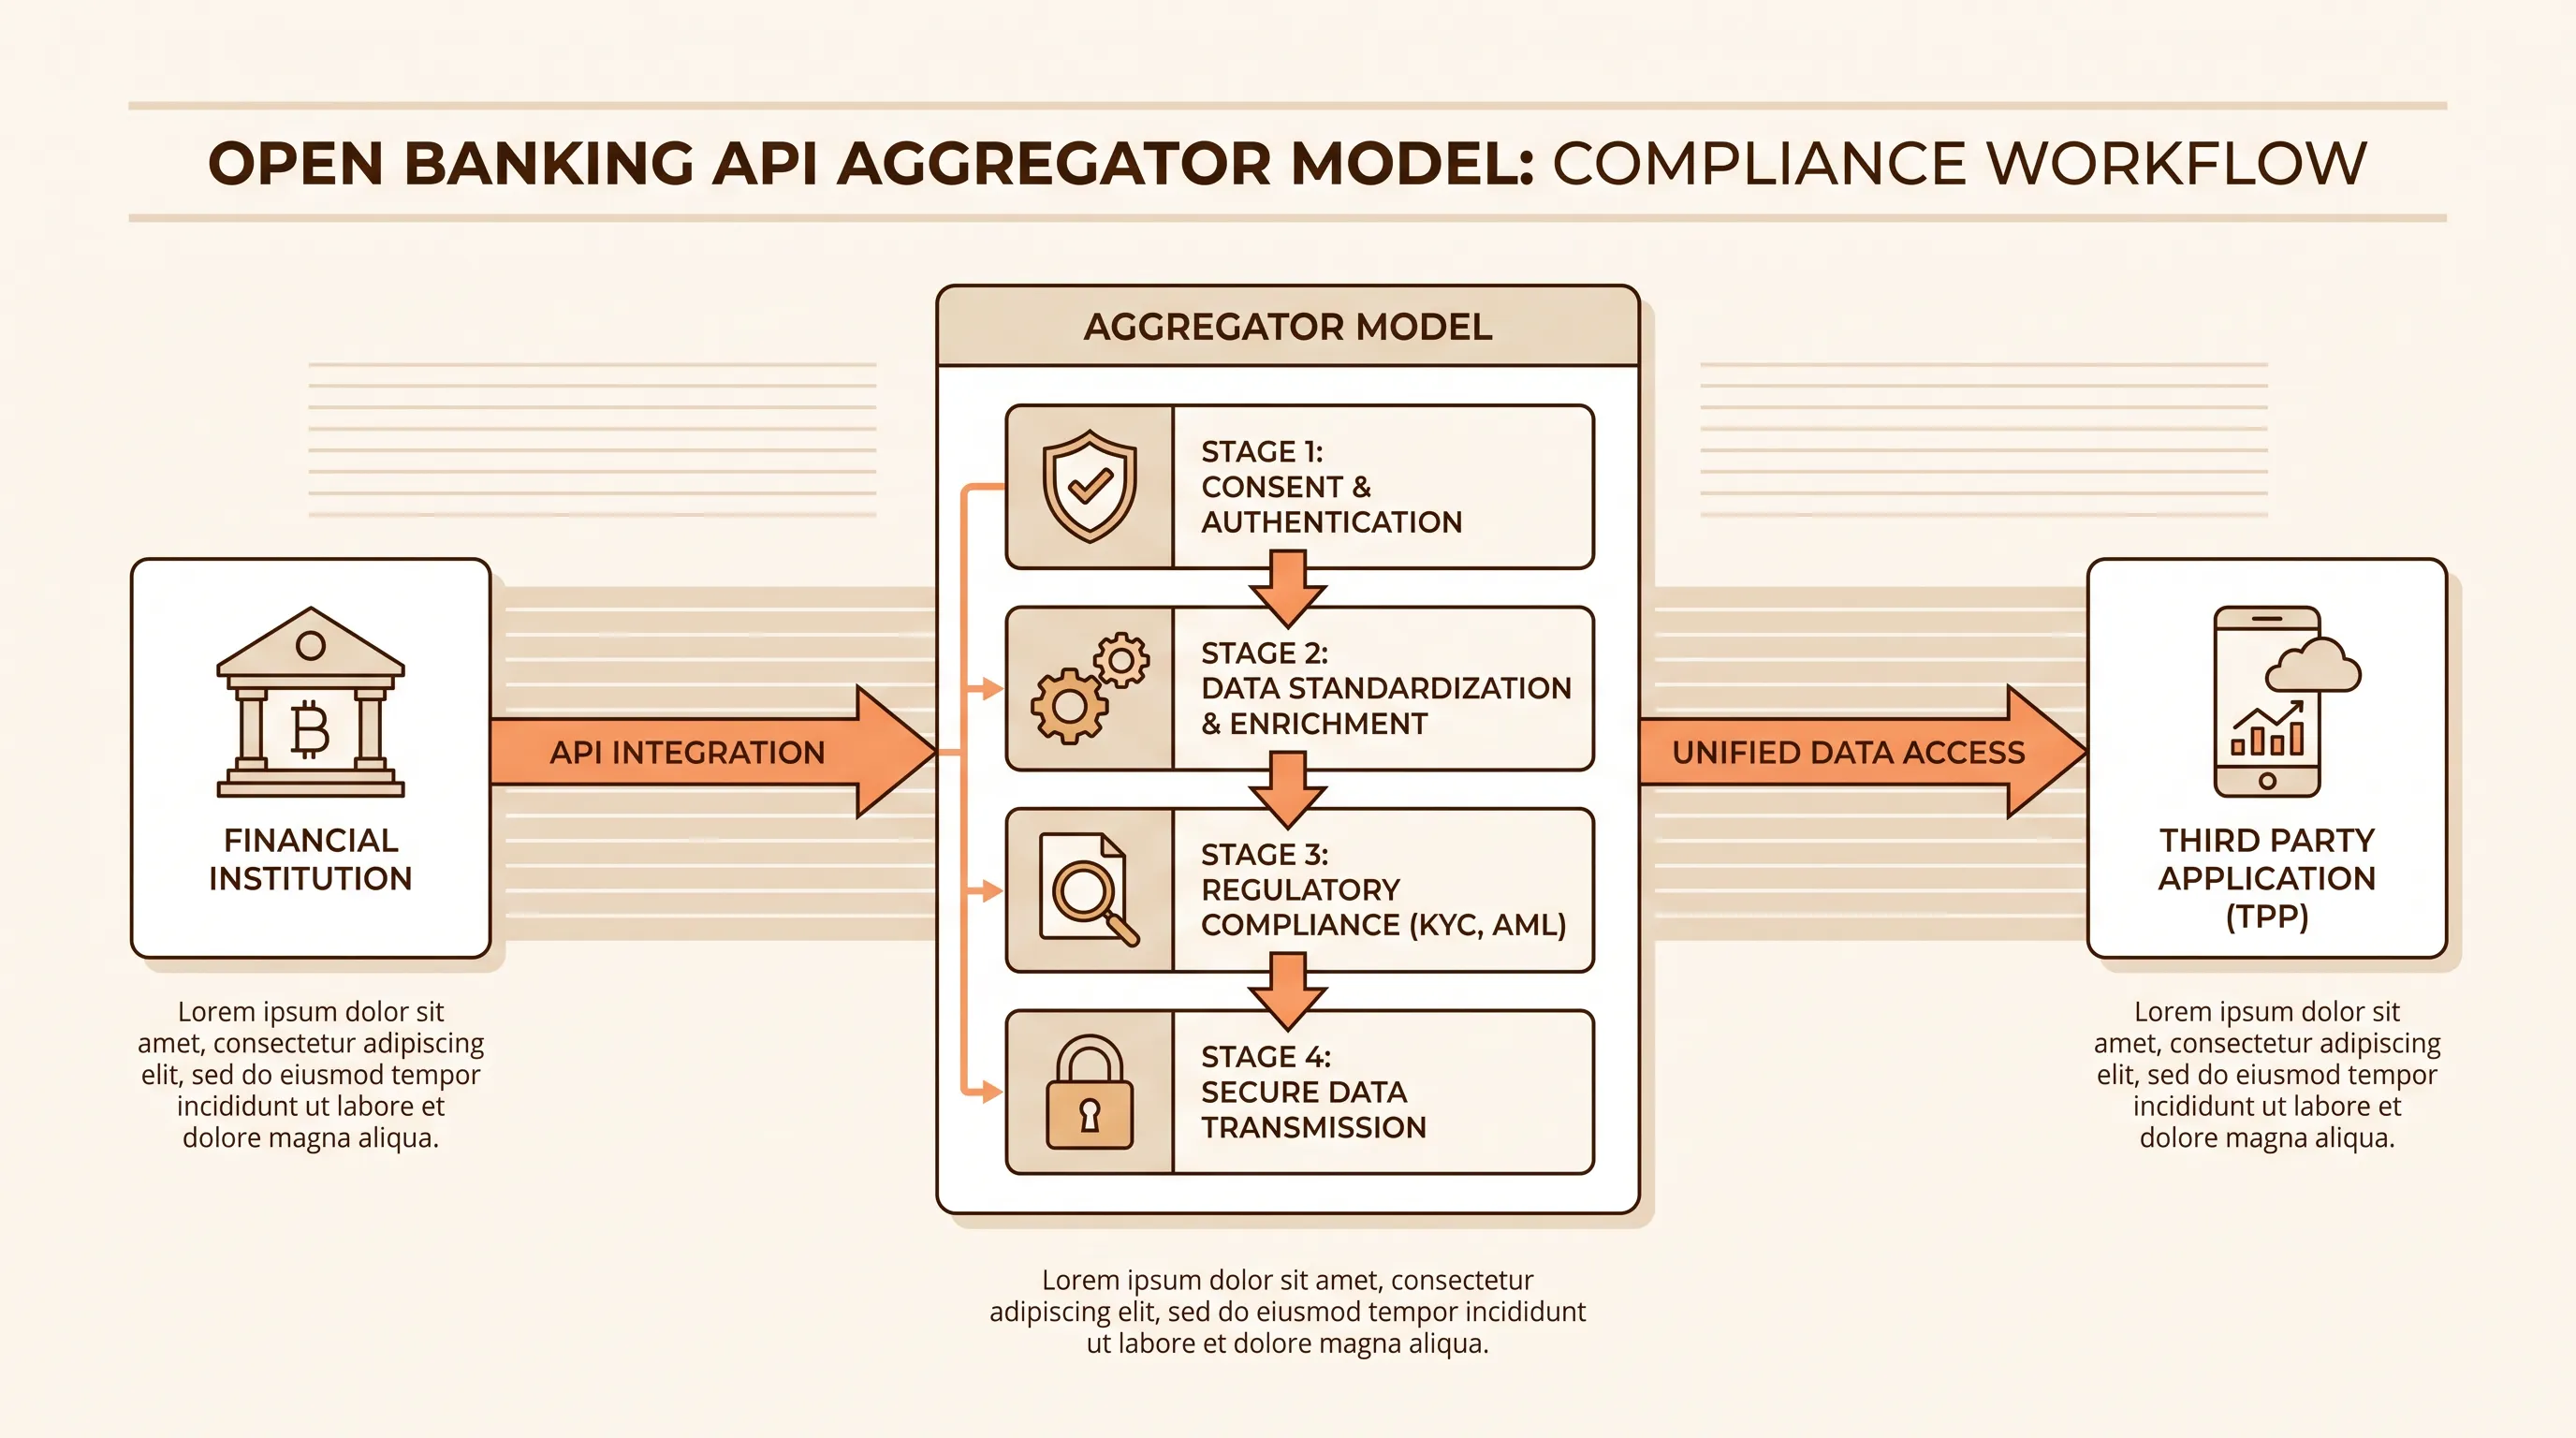
Infographic illustrating the aggregator model of open banking API integration, featuring icons for compliance checks in a structured layout.

Three models exist, and the trade-off between them is control against maintenance. You can integrate with banks yourself or buy a normalized layer over many banks. A third path is to buy a layer plus the regulatory and operational wrapper around it. Each moves work somewhere else rather than removing it.

Time to market separates them most sharply. Direct work measures in quarters per market. An aggregator gets you a sandbox connection in an afternoon and a production one in weeks. A managed arrangement adds licensing as well as consent and security controls on top, which shortens your compliance runway at the cost of a deeper dependency.

Geographic reach is where the models diverge again. Europe is not one integration surface, even under a common directive. 30 countries implement NextGenPSD2, the Berlin Group's access-to-account framework, yet the standard is a guide rather than a rulebook, and banks interpret scope differently.

Direct bank connections

Direct integration earns its cost in narrow markets. If 90% of your volume sits with four banks in one country, you're building four integrations and maintaining four, which is a tractable engineering commitment with no per-call margin stacked on top.

It also earns its cost where the bank relationship is commercial rather than incidental. A bank charging for premium data access, or offering endpoints outside the regulatory minimum, negotiates with you directly. JPMorgan and Plaid struck a paid data-access deal in September 2025, which tells you the free-by-default assumption behind many US integrations is no longer safe to build on.

The cost is permanent. Every bank changes its authentication flow or deprecates a version, and your team absorbs each one. Ponto, which connects around 2,000 banks across Europe, reported to the Berlin Group that some banks limited their API scope to the standard's guidelines even where their online channels offered more, and cited the standard as justification. Direct integration means you argue that case yourself, per bank.

Aggregator model

An aggregator gives you one contract and one schema across hundreds or thousands of banks. Salt Edge covers more than 5,000 financial institutions across 50-plus countries, while Enable Banking lists 2,500-plus connections across 29 European countries. Those are different shapes of bank connectivity coverage, and neither number tells you about depth per institution.

Normalization is the value and the risk in the same feature. When a bank returns a vague error, the aggregator has to map it into its own taxonomy, and detail gets lost in translation. Accenture's analysis of Open Banking error handling found that optional fields are often not returned or carry non-specific information, which means the abstraction sits on top of already-thin signals.

Then there's dependency. Yapily's public status page shows 16 tracked incidents since May 2025, with a median duration above 21 hours for one cluster of them. Read that as a normal operating characteristic of the model rather than a criticism, and plan your degradation path accordingly.

Ready to digitise your financial institution?

Talk to our team about your roadmap and discover scalable digital banking solutions tailored to banks, fintechs and microfinance institutions.

Request a Demo →

Managed provider model

A managed arrangement means the open banking API provider carries obligations you'd otherwise carry. That can include operating under their license and running the consent interface. Yapily states clients can operate under its licence in the UK and EU, so they avoid the cost of securing their own.

Verify each of those against the contract rather than the website. "We handle compliance" is a marketing sentence. What you need in writing is who registers you as an agent and who owns remediation when a bank connection breaks.

Under the EU's Digital Operational Resilience Act, this stops being optional diligence. Article 30 sets mandatory contractual terms for agreements with ICT providers, with additional clauses for services supporting critical or important functions. Those clauses require full service level descriptions and audit rights. If your open banking API provider supports a critical function, the contract has to say so explicitly.

Open banking API provider criteria

Feature checklists reward marketing teams. Build your criteria around artifacts instead: sandbox behavior you observed and contract language your legal team has read.

Ask for evidence in a form you can compare across bidders. A provider that won't share institution-level performance data with a serious prospect won't share it with a customer either, and that refusal is itself a data point worth recording on the scorecard.

Bank connectivity coverage

Usable bank connectivity coverage is the count of institutions where your specific journey completes for your specific customers. Everything else is a marketing number. Extract the top institutions by volume from your customer base and hand that list to each provider as the coverage test.

For each institution on your list, get answers to these:

  1. Which account types are supported, such as business accounts and credit cards, since retail current accounts are usually the only universal case.

  2. Which authentication flow the bank uses, whether redirect or embedded, and what that does to your conversion.

  3. Which data endpoints return, and how far back transaction history goes.

  4. Whether payment initiation is supported at all, and which payment types.

Bank connectivity coverage differs sharply between the data side and the payments side, and an open banking API provider rarely presents them separately unless you ask. Business account depth is the most common gap. Yapily positions deeper business account connectivity as a differentiator precisely because it isn't standard across the market.

Expansion plans belong in the contract. If your second market launches in nine months, ask for the named institutions the provider commits to supporting by then and what happens commercially if that slips.

API quality and reliability

Uptime figures need a baseline before they mean anything. The UK's CMA9 banks recorded 99.77% average API availability in one recent month at 330ms average response time, with 99.54% of calls succeeding. Your open banking API provider sits on top of that, so its own availability is the ceiling minus its own failures, never better than the banks underneath.

Latency matters differently because of where it lands. A 400ms data refresh in a background job is invisible. The same delay inside a payment authorization, stacked with a bank redirect and a mobile app handoff, is where customers abandon. Ask for percentile latency, not averages, and ask for it per journey.

Data freshness is where normalization claims get tested. Ask when transactions appear relative to the bank posting them and how pending items are represented. Then check versioning: how long deprecated versions run and whether breaking changes have ever shipped inside a minor release.

Incident transparency is easy to verify before you sign. Public status pages with historical incidents and root cause write-ups are evidence. A private status page shared only after contract signature tells you what the operating relationship will feel like.

Consent and security controls

Consent is a lifecycle. Under the amended EU technical standards, the strong customer authentication renewal cycle for account information moved from 90 to 180 days with a mandatory exemption, while the UK kept 90-day re-confirmation. If you operate in both, your consent and security controls have to handle two clocks at once.

That renewal moment is expensive when handled badly. In evidence submitted to the European Banking Authority, one third-party provider reported quarterly churn rising from just under 7% to 44% after PSD2 reauthentication came in, a jump it attributed to the 90-day rule rather than any change in its product. Open Banking Limited notes some providers push customers through a full new consent journey every 90 days when a shorter refresh was available.

Work through the consent mechanics with the provider:

  • Creation: what the customer sees and whether you control the wording.

  • Renewal and revocation: whether revocation propagates to the bank, and how fast.

  • Audit trail: what's logged and whether you can export it during a regulatory review.

On the security side, ask which profile the provider implements. FAPI 1.0 Part 2, Advanced, is the OpenID Foundation's high-security profile for read-and-write access, and it's the relevant benchmark for payment initiation. Certifications matter too, but the division of responsibility matters more, because consent and security controls split across you and the provider in ways that only appear in a shared responsibility matrix.

US teams face an unsettled rulebook here. On October 29, 2025 a Kentucky federal court enjoined the Consumer Financial Protection Bureau (CFPB) from enforcing the Personal Financial Data Rights rule until it completes reconsideration. Build your consent and security controls to the rule's intent anyway, because retrofitting an audit trail after the fact costs more than building one now.

Ready to digitise your financial institution?

Talk to our team about your roadmap and discover scalable digital banking solutions tailored to banks, fintechs and microfinance institutions.

Request a Demo →

Documentation and support

Documentation quality predicts integration cost more reliably than any other visible signal. Give a developer on your team four hours with the public docs and a sandbox key, then ask what they got working without contacting the vendor. That result is your evidence.

Sandbox realism is the part an open banking API provider oversells. Accenture points out that Open Banking's functional conformance suite mainly simulates successful transactions, because simulating failures risks the live systems. If the provider's sandbox has the same bias, you'll discover your error handling in production.

For support, get specifics into the agreement: response times by severity and who's on the escalation path at 2am. Providers describe support in tiers, and the tier you're quoted during sales isn't always the tier in the contract.

Test before committing

Run a real integration before you sign anything. Two weeks of engineering time against a sandbox costs less than one quarter of production surprises, and it converts every claim in this evaluation into something you observed.

Start with the representative journeys. Link an account and pull twelve months of transactions across your top five institutions. Initiate a payment and follow it to a terminal status. Time each step and record where users would be waiting.

Then break things deliberately:

  • Expire a consent mid-session and watch what your application does.

  • Call an institution the provider lists as temporarily unavailable.

  • Submit the same payment twice with the same idempotency key.

  • Trigger a payment failure and read the error the provider returns.

  • Compare error formats across three different banks for the same failure.

That last test is the one that surprises teams. Inconsistent error shapes across institutions are the single biggest driver of unplanned integration work, because every inconsistency becomes a conditional branch in your code that somebody has to maintain forever.

Compare full ownership costs

Pricing models in this market are not comparable line by line, which is the point. Plaid's own documentation describes three billing shapes that vary by product: a one-time fee per connected account and a monthly subscription per connected account. A third shape is a flat fee per successful API request. Two providers can quote the same headline rate and produce bills that differ by a factor of three.

Model it against your actual volume curve instead. Take your projected connected accounts and payment count for month one and month twelve. Then ask each provider to price those along with month twenty-four. Getmonetizely's analysis of published contract terms puts Plaid per-link costs between $1.50-$2.00 at low volume and $0.30-$0.60 above 50,000, so the curve, not the rate card, is what you're buying.

Then add the costs no open banking API provider quotes. Your integration engineering and the ongoing maintenance as the provider ships version changes. For a managed arrangement, add the effort of oversight, because delegating an obligation doesn't delegate accountability for it.

Market expansion pricing deserves its own line. Ask what a new country costs and whether it's a contract amendment or a rate change. Providers price expansion inconsistently, and the answer you get in negotiation is better than the one you get after signature.

Verify production responsibility

Once you're live, someone monitors availability and bank-specific incidents. Name that someone for each item, in writing, before the contract closes. Split ownership without a named owner means nobody watches.

The reason to be exact is that most of what breaks is a bank. When Barclays authentication degrades on a Tuesday, your customers blame you and your open banking API provider points at the bank. The question is whether your provider detected it and worked the remediation, or whether your support queue found out first.

So confirm the operating mechanics. Alerting thresholds and channels. Status reporting cadence and whether it's per-institution. Maintenance windows and how much notice you get. Who chases the bank, and how you'll know they did.

Exit provisions close the loop. DORA requires financial entities to maintain practical, tested exit strategies for third-party arrangements supporting critical functions, and there is no grandfathering for contracts signed earlier. Data portability and a transition period long enough to reintegrate elsewhere belong in the agreement.

Score each provider

Turn everything you gathered into a weighted scorecard tied to your launch requirements. Weight bank connectivity coverage highest if your customers are concentrated in institutions with patchy support. Weight consent and security controls highest if you're operating in two regulatory regimes at once. Weight support and documentation highest if your integration team is three people with other commitments.

Have technology and compliance stakeholders score independently against the evidence, before any group discussion. Independent scoring exposes disagreement that a shared meeting would smooth over, and the disagreements are the useful part. Where a compliance score and an engineering score diverge by three points on the same criterion, you've found something neither team had fully explained to the other.

Resolve the gaps by going back to evidence rather than argument. If nobody can settle whether the provider's error handling is adequate, that's another sandbox test. The open banking API provider you pick should win on the criteria you weighted heaviest, and you should be able to show a regulator or a board why.

One caution on the whole exercise. An evaluation this thorough takes four to eight weeks, and teams under launch pressure compress it into a demo and a reference call. Everything you skip becomes an unpriced risk carried by whoever is on call in month three.

Plan the next step

Score your shortlist before a single line of integration code is written, because the cost of switching an open banking API provider after launch is measured in quarters rather than sprints. Doocat builds and integrates banking and payments systems for banks and fintechs, which means we've worked through these provider evaluations from inside the delivery timeline rather than the sales cycle. Book a call with our team to validate your requirements and confirm the open banking API provider that fits what you're actually launching.
Ready to digitise your financial institution?

Talk to our team about your roadmap and discover scalable digital banking solutions tailored to banks, fintechs and microfinance institutions.

Request a Demo →

Review the master services agreement, data processing agreement, service-level schedule, subprocessor list, and exit terms before selection. Check that each document names incident duties, audit access, data return format, retention periods, and liability boundaries. Website claims don't establish obligations, so score only commitments that appear in contract language.

Yes, if the added resilience or bank coverage justifies the extra operating work. A dual-provider setup requires clear routing rules, duplicate-payment safeguards, consent records that identify the source, and reconciliation across both APIs. Test failover by institution, since a second provider can't fix an outage at the underlying bank.

Ask where the provider stores, processes, backs up, and supports access to customer data. Obtain the current subprocessor list and identify each transfer outside your operating region. Your privacy team should confirm that the proposed transfer mechanism, retention period, and deletion process meet the rules that apply to your customers.

Test the exit plan before contract signature when the provider supports a critical service. Request a sample export, verify that consent and transaction records have usable identifiers, and estimate the time to load them into a replacement system. A contractual portability clause isn't enough if the data can't be reconciled.

Doocat can review launch requirements, assess evidence from shortlisted vendors, and help teams test an open banking API provider in a sandbox. A call is useful when engineering and compliance scores conflict, because the discussion can identify the missing contract evidence or test case needed for a decision.

Schedule a Meeting

Book a time that works best for you

You Might Also Like

Discover more insights and articles

Two branch managers discuss data visualizations at a workstation, surrounded by monitors in a collaborative office environment.

How African MFIs Can Improve Regulatory Reporting Accuracy

Accurate regulatory returns come from control. Standardize definitions across branches and map every reported field to a named source system. Technology helps only after those definitions and controls exist.

A finance team of three professionals discusses credit submission processes around a modern conference table in a bright office.

Credit Bureau Reporting in Kenya: A Practical Guide for Lenders

This article walks through the operational side of credit bureau reporting in Kenya: what you submit each cycle and how to validate it. It then covers what to do when records bounce back and which evidence to keep for your next examination. It's written for the teams that build and sign off on the monthly file.

A financial consultant in business attire engages with a tablet in a modern office, surrounded by natural light and sleek furniture.

Build vs Buy for Digital Banking: What Banks Should Compare Before Deciding

Compare build and buy across the full lifecycle. Score both paths on total multi-year cost and credible time-to-market. Delivery risk and internal capacity belong in that score, as do control and who funds compliance changes after launch. Building wins only when a capability creates real differentiation your institution can staff and maintain for years.

Modern executive office workspace featuring an organized desk with a laptop, documents, and natural elements, illuminated by golden-hour light.

Microfinance Software for MFIs: Core Banking, Lending, Mobile, and Reporting

This article explains what a unified system for a microfinance institution actually has to do, capability by capability, from client records through regulatory reporting. It also lays out how to test product fit against your own workflows before you sign anything.